LLM Laundering For Security
- Date:
- Last Updated:
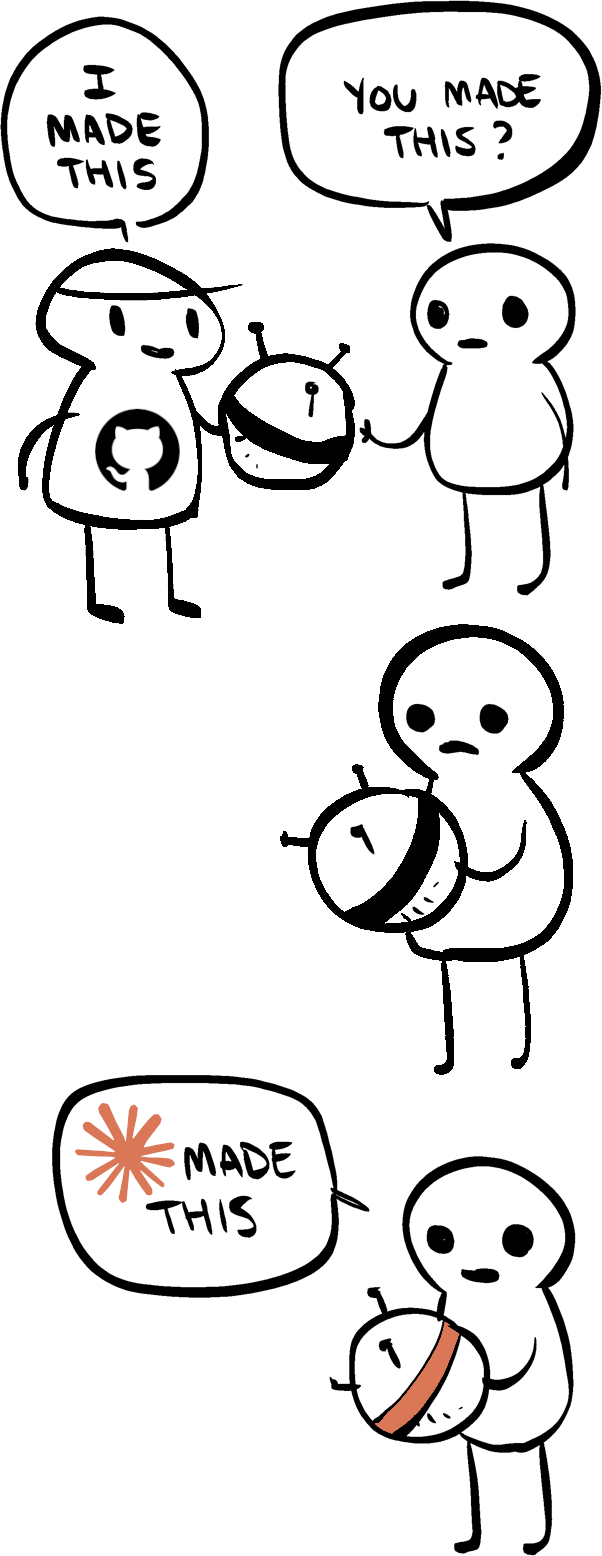
I recently started using the Pi agent harness. It is developed with a plugin-oriented ethos of minimalism. There is a vibrant ecosystem of plugins you can use, but I am not a fan of installing tons of community packages on my systems for security reasons. When I look at the files on GitHub, even many of the simplest plugins have a minimum of a dozen files. Admittedly, most of those files are metadata or other minutiae, but I am not a JavaScript or TypeScript developer, so I do not have a good grasp of how package.json and package-lock.json work, and I do not understand when downloading (or updating) a package from NPM might result in arbitrary code execution before I can audit the files. As the left-pad incident showed, many developers are wont to include packages for the simplest things, so even if the core code of the extensions I am interested in is small, their dependency tree could end up being quite complicated. The solution I've decided to lean on is simple: if I find a plugin I want to use, I will simply have Claude replicate its functionality. I have avoided having LLMs write large amounts of code for me for personal projects, but I see Pi extensions as a means to an end: what I care about most is getting something that works. Right now, I am not interested in learning the ins and outs of an entire programming language ecosystem just so I can configure a tool I want to use. At some point that may change, but in the meantime, I am going to continue feeding feature descriptions and README files into Claude to get what I want.
I should note that the meme attached to the post is not entirely accurate. Some of the plugins I'm replicating have clearly been vibe coded, so the GitHub logo on the first person's shirt could have been a Claude logo.
Another, unintended, interpretation of the comic would be commentary on rejecting vibe coders' dubious claims to ownership and copyright.